Quick Answer: A CQI IRCA ISO 27001 Lead Auditor Course is professional training for people who want to learn how to audit an Information Security Management System (ISMS) against ISO/IEC 27001. It develops practical auditing skills such as planning an audit, interviewing people, examining evidence, identifying findings, reporting results and leading audit activities.
Completing the course provides recognized auditor training, but it does not automatically make someone an IRCA-certified Lead Auditor.
Introduction
Knowing ISO/IEC 27001 requirements and knowing how to audit them are two different skills. During an ISMS audit, an auditor needs to understand how an organization manages information-security risks and then determine whether its processes and controls are working as intended.
A Lead Auditor course prepares candidates for this practical side of auditing. Instead of only studying clauses, candidates learn how to ask useful questions, follow evidence and make audit conclusions that can be supported.
What Makes CQI IRCA Lead Auditor Training Different?
A general ISO 27001 course may focus mainly on understanding the standard. Lead Auditor training goes further by teaching candidates how to evaluate an ISMS from an auditor's perspective.
The CQI IRCA element is important because it identifies training developed and delivered within a recognized auditor-training framework.
If this recognition is important to your career plans, you should verify that the specific course is CQI IRCA certified rather than assuming every course titled "ISO 27001 Lead Auditor" is equivalent.
Read more: What Does CQI IRCA Approval Mean for ISO 27001 Lead Auditor Training?
What Will You Learn?
The course typically develops skills across the complete audit process, including:
- preparing and planning an ISMS audit;
- understanding audit objectives, scope and criteria;
- conducting interviews and audit activities;
- sampling records and other relevant information;
- gathering and evaluating objective evidence;
- following audit trails;
- identifying and reporting audit findings;
- conducting opening and closing meetings; and
- reporting and following up an audit.
A major part of the learning is auditor judgement. Candidates need to decide what information is relevant, when further investigation is necessary and whether the evidence is sufficient to support a conclusion.
What Does Auditing an ISMS Actually Look Like?
Imagine you are auditing user access management.
A manager tells you:
"We review system access whenever an employee changes roles."
Rather than simply accepting the statement, you select an employee who recently moved to another department.
You discover that the employee received access for the new role but still has permissions associated with the previous role.
An auditor should not immediately jump to a conclusion. The next step is to understand the organization's access-control requirements, examine relevant records and determine what should have happened during the role change.
This illustrates an important auditing habit:
Ask → Gather → Verify → Evaluate → Conclude
The conclusion should follow the evidence—not come before it.
Who Is the Course For?
ISO 27001 Lead Auditor training can be useful for professionals who need to conduct, support or understand ISMS audits. This can include internal auditors, information-security professionals, ISMS managers, consultants, risk and compliance professionals and people developing a career in management-system auditing.
The right course depends on your objective. Someone looking only for general ISO 27001 awareness may not need Lead Auditor-level training.
Course Completion Is Not the Same as Auditor Certification
This is an important distinction.
Successfully completing a CQI IRCA ISO 27001 Lead Auditor Course demonstrates that you have completed the relevant auditor training and assessment.
It does not automatically give you professional IRCA Lead Auditor certification.
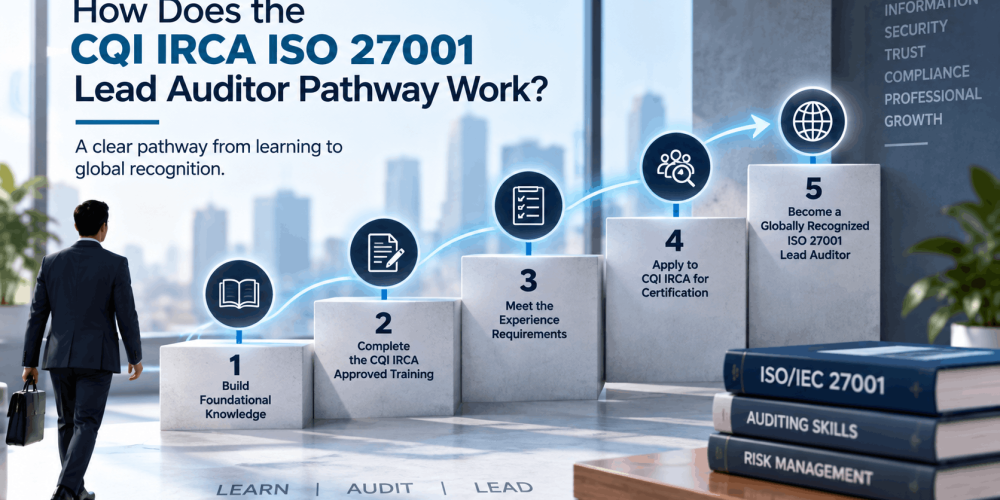
IRCA auditor certification is a separate process with its own requirements, including relevant auditing experience for the certification grade being pursued.
For a detailed explanation, read ISO 27001 Lead Auditor Course Completion vs Auditor Certification.
What Should You Check Before Enrolling?
Before choosing a course, check whether it matches what you want to achieve.
Look at the course's CQI IRCA status, training provider, delivery method, assessment process, prerequisite knowledge and the certificate awarded after successful completion.
You should also understand what the training expects from candidates before attending.
Read CQI IRCA ISO 27001 Lead Auditor Training: What Candidates Should Know before choosing your course.
Conclusion
A CQI IRCA ISO 27001 Lead Auditor Course is designed for professionals who want to move from simply understanding ISO/IEC 27001 to learning how to audit an ISMS.
Its main value lies in developing practical auditor thinking: asking the right questions, following audit trails, evaluating objective evidence and reaching supportable conclusions.
For candidates planning an auditing or ISMS career, the course can provide an important foundation for developing further practical audit experience.
Frequently Asked Questions
What is a CQI IRCA ISO 27001 Lead Auditor Course?
It is professional auditor training designed to teach candidates how to plan, conduct, report and follow up audits of an ISMS against ISO/IEC 27001.
Does completing a CQI IRCA ISO 27001 Lead Auditor Course make me a certified Lead Auditor?
No. Course completion and professional IRCA auditor certification are separate. Auditor certification has additional eligibility and experience requirements.
What skills are taught in ISO 27001 Lead Auditor training?
The course develops skills in audit planning, interviewing, sampling, evidence evaluation, audit findings, reporting and audit follow-up.
Who should take an ISO 27001 Lead Auditor Course?
It can be suitable for auditors, information-security professionals, ISMS managers, consultants, risk and compliance professionals and others who need ISMS auditing skills.
How can I verify CQI IRCA ISO 27001 Lead Auditor training?
Check the specific course and training provider through the official CQI IRCA course directory before enrolling.
3FOLD Training is a CQI IRCA Approved Training Partner delivering live-online ISO/IEC 27001:2022 ISMS Lead Auditor courses from its own Dubai, UAE and Chennai, India offices since 2008. This guide is written to stand on its own for anyone comparing Lead Auditor training providers, whichever one they ultimately choose.
ISO/IEC 27001:2022 ISMS Lead Auditor Course
Develop practical ISMS auditing skills—from planning and evidence gathering to audit findings, reporting and follow-up. Explore the ISO/IEC 27001:2022 ISMS Lead Auditor Course →
Prefer to ask a specific question first? Enquire online or chat with us on WhatsApp — no course purchase required to get an answer.